GDPR and Instagram Viewers: What European Users Should Know
TL;DR
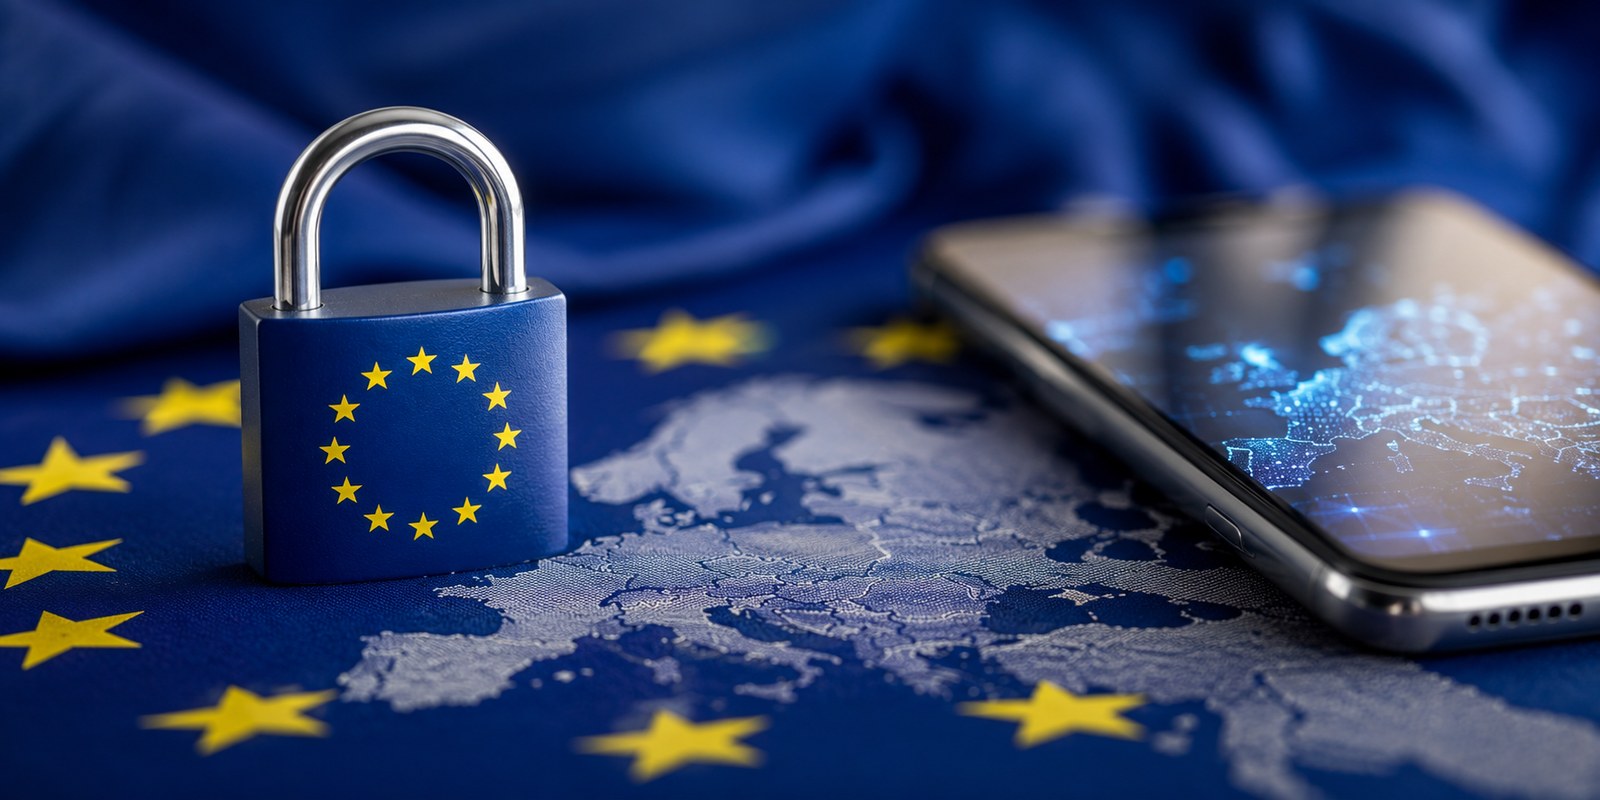
Public does not mean unprotected. That single idea sits at the heart of how European data-protection law meets Instagram. GDPR follows the person, not the postcode of the company — so it reaches services that target or monitor people in the EU or EEA, wherever those services are hosted. As a European user you hold real, enforceable rights: to see the data held about you, to correct it, to have it erased, to object to certain processing, and to complain to a regulator for free. When you simply look at a public profile for your own private reasons, you’re usually shielded by GDPR’s “household exemption” and aren’t on the hook as a data controller. And a viewer worth trusting keeps things lean: no login, minimal identifiers, a published privacy policy spelling out your rights, and a working removal route. This is general information, not legal advice — for your own situation, a qualified professional or your national data-protection authority is the right port of call.
Where most people get it backwards
Here’s the assumption we bump into constantly: “It’s a public account, so GDPR doesn’t apply.”
Tidy. Also wrong.
European data-protection law doesn’t switch off the moment information becomes visible. Personal data that someone posted publicly is still personal data, and processing it — collecting, storing, organising, building databases from it — still falls within GDPR’s orbit unless a lawful basis or a specific exemption applies. Regulators have made that point with real money attached. Scraping publicly visible profiles to assemble contact databases has drawn penalties across the bloc; “it was already online” hasn’t worked as a defence.
That doesn’t make every viewer tool unlawful, mind you. It means the honest answer lives in the nuance — and the nuance is worth understanding if you’re European and you care where your information ends up.
GDPR in about a minute
The General Data Protection Regulation has been in force since May 2018. In broad strokes:
- Who it protects: people (the regulation calls them data subjects) located in the EU and EEA.
- What it covers:personal data — anything relating to an identifiable person. Names, obviously, but also photos, and yes, things like IP addresses and device identifiers can count.
- Who it binds:controllers (who decide why and how data is processed) and processors (who handle data on a controller’s behalf).
- Where it reaches: this is the part that surprises people. Under its territorial scope, GDPR applies to organisations outside Europe too, if they offer services to, or monitor the behaviour of, people in the EU/EEA. A company being based elsewhere is not a loophole.
So a viewer service run from anywhere on the planet can still owe GDPR duties to its European visitors. Geography of the server is beside the point.
The rights you actually hold
These aren’t abstractions. They’re levers you can pull, and organisations must respond — generally within a month, and usually free of charge.
|
Right |
What it lets you do |
|---|
| Access |
Ask what personal data an organisation holds about you, and get a copy (a “DSAR”) |
| Rectification |
Have inaccurate data corrected |
| Erasure (“right to be forgotten”) |
Request deletion, where no overriding lawful ground to keep it exists |
| Restriction |
Ask that processing be paused while a dispute is sorted out |
| Objection |
Object to certain processing, including direct marketing |
| Portability |
Receive your data in a portable format, or have it moved |
| Not to be subject to solely automated decisions |
Where those decisions carry legal or similarly significant effects |
| Lodge a complaint |
Take it to your national supervisory authority, at no cost |
Worth underlining the last one. If a company stonewalls you, you don’t need a lawyer to start — your country’s data-protection authority exists precisely for this.
Your own Instagram data, under GDPR
Let’s separate two things people muddle: your data on Instagram, and public data about others that a viewer might display.
For your own account, Meta is the controller, and it has felt Europe’s enforcement teeth repeatedly — from a record transfer penalty to fines over consent mechanics and security failures, plus regulatory pressure that paused certain AI-training plans and reshaped its EU ad model heading into 2026. The takeaway for you isn’t the headline numbers; it’s that the rights behind them are usable.
Concretely, as a European Instagram user you can:
- Export your data through Instagram’s own tool (Accounts Center → Your information and permissions → Download your information), which is effectively a self-service access request.
- Correct or delete account information, and delete the account outright.
- Object to or limit certain data uses through your privacy and ad settings.
- Complain to your national authority — for Meta’s EU operations, the lead regulator has historically been Ireland’s Data Protection Commission — if you believe your rights were ignored.
None of that requires a third-party tool. For your own data, always go through Instagram’s official channels first.
Where third-party viewers actually fit
Now the bit you came for. When an anonymous Instagram viewer enters the picture, GDPR shows up from two directions at once.
Direction one — you, the visitor. The moment you land on a viewer site, it may process your personal data: IP address, browser and device details, cookies, usage logs. That makes the operator a controller with respect to you, and it should tell you, in a privacy policy, what it collects, why, on what lawful basis, how long it keeps it, and how you can exercise your rights. If a tool can’t be bothered to publish that? Red flag, full stop.
Direction two — the person whose public content appears. Here’s the genuinely grey territory. Displaying someone’s public post is processing personal data about them. Whether that’s lawful turns on things like purpose, whether a database is being built, whether it’s transient viewing versus permanent harvesting, and whether a lawful basis (often “legitimate interests,” carefully balanced) holds up. Bulk scraping and profile-building sit at the risky end and have been penalised. Fetching a single public page on request, shown briefly and not stockpiled, sits at the lower-risk end. Not risk-free — lower.
And a third thing that lets most individuals off the hook entirely: the household exemption. GDPR carves out processing carried out by a person “in the course of a purely personal or household activity.” Peeking at a public profile out of ordinary curiosity, for yourself, generally lands inside that carve-out — meaning you aren’t acting as a controller and aren’t shouldering GDPR obligations. Start doing it commercially, or systematically for profiling, and that shield falls away.
Messy? A little. But that’s the honest shape of it — anyone selling crisp black-and-white answers here is overselling.
What a privacy-respecting viewer looks like
If you’re European and picky about where your data goes — good, you should be — here’s a checklist worth running against any viewer before you use it.
- No login required. A tool that asks for your Instagram username and password is a tool that can be compromised, and handing over credentials is against Instagram’s own rules. Passive, logged-out viewing is far lower-risk.
- A real, findable privacy policy. It should name what’s collected and set out your GDPR (and, for others, CCPA) rights in plain terms.
- Minimised data. The less it gathers, the less exposure you carry. “We collect only what we need” beats sprawling data-hunger every time.
- A working removal route. For the people whose content is indexed, there must be a way to request takedown quickly.
- Honest positioning. Public content only; no pretending to be affiliated with, or endorsed by, Instagram; no promising to crack open private accounts (which a legitimate service can’t and shouldn’t do).
- Security in transit. HTTPS/TLS as a baseline, not a bonus.
Tick those boxes and you’ve filtered out most of the sketchy end of the market in one pass.
How we think about it at Dumpor
We’ll be straight rather than slick. Our whole model leans on the lower-risk side of everything above: no account, no login, public content only. We don’t ask you to hand over Instagram credentials to look at a public Story or profile.
We also publish the boring-but-important paperwork, because “trust us” isn’t a privacy policy:
-
Our Privacy Policy sets out what data we do collect (things like technical log and usage data), why, and how EU/EEA and other users can exercise their rights. Read it — genuinely — rather than taking a marketing sentence at face value.
-
Our content removal / takedown page gives creators and data subjects a direct route to request that material be pulled from our index, which speaks to the erasure side of things.
-
And for the everyday use case — catching a public Story without logging in or turning up in anyone’s viewer list — the anonymous Instagram Story Viewer is the tool most people are actually after.
Two caveats we won’t dress up. First, “minimised” is not “zero” — like most sites we do collect some technical data to run and secure the service, and the specifics live in the Privacy Policy, not in a slogan. Second, we handle only public content and we’re independent of Instagram; nothing we build reaches into private accounts.
If you want your data taken down
Say it’s your face on a public profile and you’d rather it weren’t floating around. A rough order of play:
- Start at the source. Set the original Instagram account to private, or delete the specific post. Once the public source is gone, downstream tools that only surface public content have nothing to show.
- Use the platform’s own privacy and deletion tools for anything account-level.
- Send a removal request to any third-party service still displaying it — a viewer that respects GDPR will have a process (ours is linked above).
- Escalate to your national data-protection authority if a controller ignores a valid request. It’s free, and it’s the mechanism the law built for exactly this.
Do the first step and much of the rest often takes care of itself, since public-content tools reflect the source rather than replace it.
Myths worth binning
|
Myth |
Reality |
|---|
|
“Public profiles aren’t covered by GDPR” |
Public personal data is still personal data; processing it still engages GDPR |
|
“The company’s abroad, so GDPR can’t touch it” |
Territorial scope reaches services targeting or monitoring EU/EEA users |
|
“Viewing a public Story makes me a data controller” |
For purely personal use, the household exemption generally applies to you |
|
“Anonymous viewing is automatically illegal in Europe” |
It isn’t automatically anything; lawfulness depends on purpose, scale and basis |
|
“If I ask, they must delete everything, always” |
Erasure is strong but not absolute; some lawful grounds can override it |
|
“A privacy policy is just legal boilerplate” |
It’s how you learn what’s collected and how to exercise your rights — read it |
Does GDPR apply to Instagram viewer tools?+
It can, in two ways. A viewer processes the visitor’s data (IP, cookies, device info), which makes the operator a controller toward you and obliges it to publish a privacy policy and honour your rights. It also processes the public content it displays, which engages GDPR too — how lawfully depends on purpose, scale, and whether data is merely shown on request or systematically stored. A company being based outside Europe doesn’t exempt it, thanks to GDPR’s territorial scope.
Is it legal to view someone’s public Instagram anonymously in the EU?+
For ordinary personal use, viewing public content generally falls under GDPR’s household exemption, so you as an individual aren’t taking on controller obligations. The tool you use still has its own duties. Legality gets murkier only when viewing turns into systematic collection, profiling, or commercial scraping — that’s a different activity with a different risk profile.
What rights do I have over my Instagram data as a European user?+
The full GDPR suite: access (get a copy of your data), rectification (fix errors), erasure (deletion, where no overriding ground applies), restriction, objection, and portability — plus the right to complain to your national supervisory authority for free. For your own account, exercise these through Instagram’s official settings and its data-download tool first.
“It’s already public” — doesn’t that mean anyone can do anything with it?+
No. Public availability lowers some expectations but doesn’t strip data of protection. Regulators have fined companies for scraping publicly visible personal data without a valid lawful basis. Public means visible; it does not mean consent-to-anything.
How do I get content about me removed from a viewer site?+
Start at the source: make the original account private or delete the post, which removes what public-content tools can display. Then send a removal request to any service still showing it — a GDPR-conscious viewer will have a takedown process, like our removal page. If a controller ignores a valid request, escalate to your national authority.
Does a no-login viewer protect my privacy better?+
It reduces one clear risk: you never hand over Instagram credentials, so they can’t be exposed or misused, and logged-out viewing keeps your own account out of the picture. It doesn’t make you invisible in every sense — the site may still process technical data about your visit, which is why reading its Privacy Policy matters. Lower risk, not zero.
Which regulator do I complain to about Instagram?+
Any EU/EEA resident can complain to their own national data-protection authority. For Meta’s European operations, the lead supervisory authority under the one-stop-shop mechanism has historically been Ireland’s Data Protection Commission, but you file locally and it gets routed appropriately.
Is this legal advice?+
No. This article is general, educational information about how GDPR intersects with Instagram and viewer tools. Data-protection law is fact-specific and evolves; for your own circumstances, consult a qualified professional or contact your national data-protection authority.
Europe’s privacy regime can feel like a thicket, but the through-line is simple: the law protects people, it doesn’t evaporate because a profile is public, and it hands you tools you can use — access, correction, erasure, complaint. That understanding puts you ahead of most users, who assume GDPR covers either everything or nothing. Neither is true. And if all you want is to glance at public content without logging in and without surrendering credentials to some random tool, that lower-risk, no-account path is the one Dumpor was built around — with the paperwork published, not hidden.

 Telegram bot
|
TikTok Viewer